- Lower Kabete Rd, Nairobi 00100, Kenya
- Mon-Fri, 08:00am - 06:00pm
- +254 (798) 586113 +254 (728) 922269
- info@afriqsilicon.com
3 Min Read
Keycloak Multitenancy Approaches for SaaS
Learn how to implement Keycloak multitenancy for SaaS platforms, with practical patterns for realms, groups, clients, and identity‑provider federation.
Learn how to implement Keycloak multitenancy for SaaS platforms, with practical patterns for realms, groups, clients, and identity‑provider federation.
What is Multitenancy in Identity Management?
In today’s cloud‑native applications, Keycloak multitenancy is essential when you need to serve multiple organisations, departments, or clients from a single platform. This pattern is core to our Multi‑Tenant Platform Development work. Multitenancy in SaaS identity management lets each tenant keep its own user base and configuration inside the same Keycloak instance.
Keycloak is an open‑source identity and access management solution that offers SSO, authorization, and identity management. It supports OAuth2, OpenID Connect (OIDC), and SAML, making it ideal for cloud‑native identity needs.
In this post we explore the approaches we use at Afriq Silicon for implementing Keycloak multitenancy (OIDC). The guide assumes basic familiarity with Keycloak terminology.
Separate Realms Per Tenant
This is the most straightforward way to achieve strong isolation. Each tenant receives its own Realm, a separate namespace for users, roles, clients, and authentication flows.
Advantages
- Full isolation lets you customise branding, login flows, and policies per tenant.
- Realm ID can serve as the tenant identifier in downstream databases.
Drawbacks
- Managing many realms adds operational overhead and increases resource consumption.
Shared Realm with Tenant‑Specific Roles or Groups
A single realm serves all tenants, while differentiation is done through Roles or Groups. Users are assigned roles or placed in groups that correspond to their tenant.
Advantages
- Simpler administration and lower resource use.
- Centralised configuration eases updates.
Drawbacks
- Isolation is weaker; you must implement detailed authorization rules to keep tenant data separate.
Partitioning with Realms and Clients
Create separate Clients for each tenant within a single realm. Each client defines its own redirect URIs, roles, and login settings.
Advantages
- Client‑level isolation keeps most settings separate while sharing the realm’s core configuration.
- Easier to provision new tenants via the Admin REST API.
Drawbacks
- Shared realm settings can still lead to cross‑tenant leakage if not carefully managed.
Identity Provider Federation for Multitenancy
Keycloak can delegate authentication to external providers per tenant (e.g., LDAP, Azure AD). This lets tenants use their own identity sources while you retain centralised access control.
Advantages
- Flexibility to integrate existing directories.
- Reduces the need to migrate user data into Keycloak.
Drawbacks
- Adds complexity and potential points of failure in the authentication chain.
Best Practices for Implementing Keycloak Multitenancy
- Automate tenant provisioning – Use the Keycloak Admin REST API to create realms, clients, and users programmatically.
- Plan for scaling – Large‑scale deployments benefit from clustering and horizontal scaling, especially with the realm‑per‑tenant model.
- Enforce isolation with RBAC – Define tenant‑specific roles and policies to keep data separate while enabling SSO within each tenant.
- Monitor per tenant – Integrate with observability tools such as Prometheus and Grafana to trace performance and errors to individual tenants.
- Consider procurement and team size – Choose the approach that matches your organisation’s procurement rules and engineering capacity; a shared‑realm model often suits thin teams with limited budgets.
Ready to build a secure, scalable multi‑tenant SaaS? Contact Afriq Silicon to discuss how we can design, implement, and operate your Keycloak‑based identity solution.
Frequently Asked Questions
Common questions on this topic, answered by the Afriq Silicon team.
What is multi-tenancy in a SaaS application?
What are the main multi-tenancy patterns?
Why use Keycloak for SaaS identity management?
How does Keycloak handle tenant isolation?
Is Keycloak suitable for enterprise-scale SaaS?
Related Services
Working through this problem? These are the services we offer that connect to it.
Multi-Tenant Platform Development
Platforms that scale from first deployment to millions of users.
Multi-tenant platform development from Afriq Silicon. We build platforms with tenant isolation, subscription billing, enterprise SSO, and resilient infrastructure.
Explore serviceSystem Orchestration
Make your infrastructure invisible, reliably fast, quietly resilient.
IT system orchestration and infrastructure from Afriq Silicon. We design scalable, secure, integrated IT environments for growing organizations.
Explore serviceRelated
Similar Articles
Stay Informed with Our Latest Articles: Explore the most recent insights, trends, and updates from our industry experts. Dive into a wealth of knowledge to keep you ahead in the ever-evolving tech landscape.
June 11th, 2026
Scalable IT Infrastructure: What It Actually Takes
Scalability sounds simple until you need it. Then it becomes the most expensive problem you didn't plan for.
September 22nd, 2026
Designing Multi‑tenant SaaS for Kenyan Banking Compliance
Learn which multi‑tenant architecture fits Kenyan banking regulations, including data residency, KYC handling, and the trade‑offs of shared vs isolated
October 15th, 2025
How Fintech Automation Is Reshaping African Finance
From mobile money to CFO automation, fintech is quietly rewiring how African businesses handle money. Here is what is changing, why now, and where to start.
November 6th, 2023
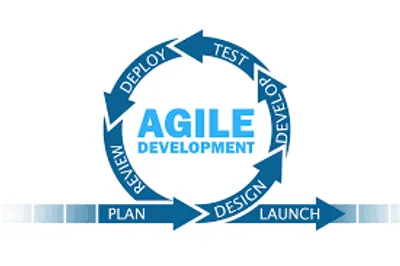
Agile Development at Afriq Silicon
How we actually run two-week sprints, and the deployment pipeline that makes each increment something you can click on rather than a status update.


Pages
- - Work
- - Services
- - Our Process
- - Contact Us
Solutions
- - Acts ML
- - Kilelehub
- - Other Projects
Legal
Contact
- - Lower Kabete Rd, Nairobi 00100, Kenya
- - Mon-Fri, 08:00am - 06:00pm
- - +254 (798) 586113
- - +254 (728) 922269
- - info@afriqsilicon.com